Solution Cross-industry
Security Copilot for the SOC
Give security analysts an AI assistant that summarizes incidents, guides investigations and drafts response, cutting time to respond.
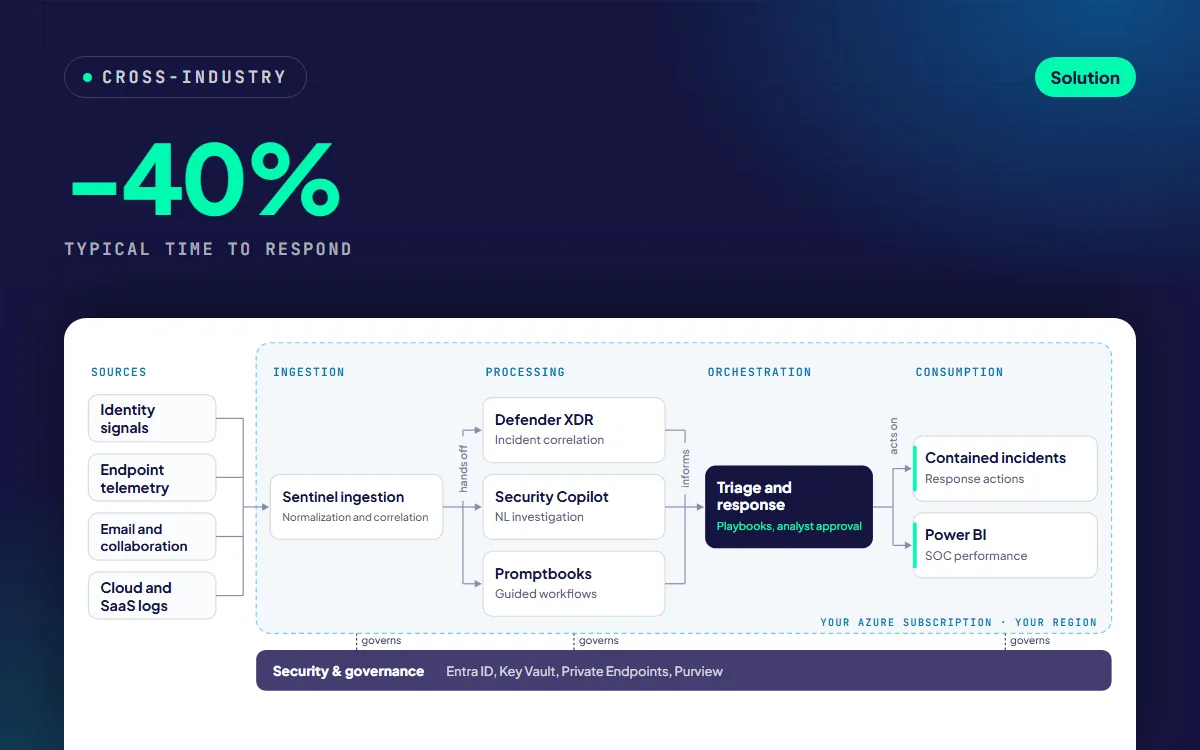
-40%Typical time to respond
FasterIncident triage and hunting
ConsistentGuided investigations
Typical outcomes for this kind of engagement. Results depend on your data and starting point.
THE CHALLENGE
SOC analysts face more alerts than any team can triage, and the work that matters (correlating signals across identity, endpoint, email and cloud) is slow, manual and dependent on the most experienced person on shift.
- Alert volume exceeds analyst capacity, so genuine incidents wait in the queue
- Correlating identity, endpoint, email and cloud signals is manual and slow
- Incident documentation consumes hours that should go to containment
OUR APPROACH
CloudGate deploys Microsoft Security Copilot integrated with Microsoft Sentinel, Defender XDR, Intune and Entra ID, so analysts can investigate in natural language across every connected signal.
- Security Copilot integrated across Sentinel, Defender XDR, Intune and Entra ID
- Custom promptbooks for phishing, identity compromise, ransomware and malware analysis
- Natural-language investigation and hunting across all connected signals
MORE LIKE THIS